Statistic about HTTP security response headers usage
📅 Last update: 09/13/2026 at 07:11:08 - Domains analyzed count: 250000.
Global usage of secure headers
Provide the distribution of usage of secure headers across all domains analyzed.
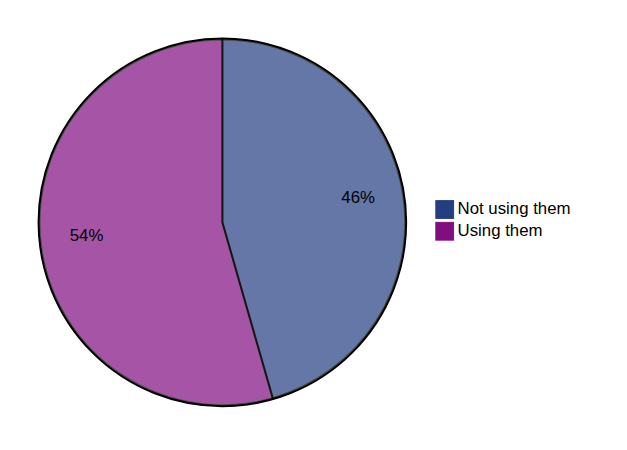
Global usage of header ‘cache-control’
Provide the distribution of usage of the header ‘cache-control’ across all domains analyzed.
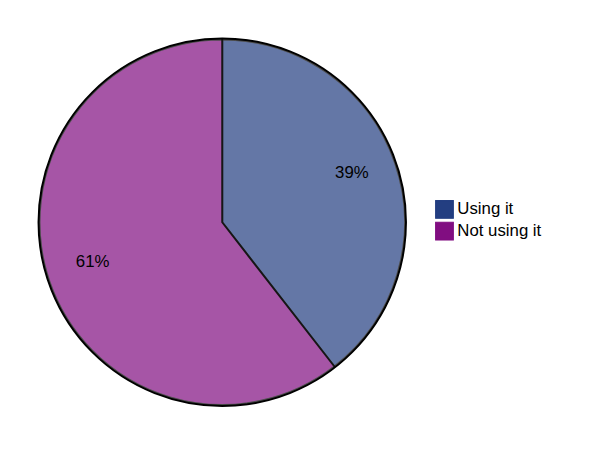
Global usage of header ‘clear-site-data’
Provide the distribution of usage of the header ‘clear-site-data’ across all domains analyzed.
Global usage of header ‘content-security-policy’
Provide the distribution of usage of the header ‘content-security-policy’ across all domains analyzed.
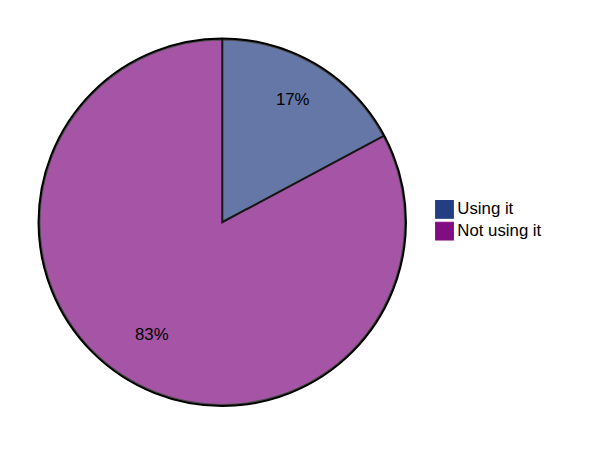
Global usage of header ‘content-security-policy-report-only’
Provide the distribution of usage of the header ‘content-security-policy-report-only’ across all domains analyzed.
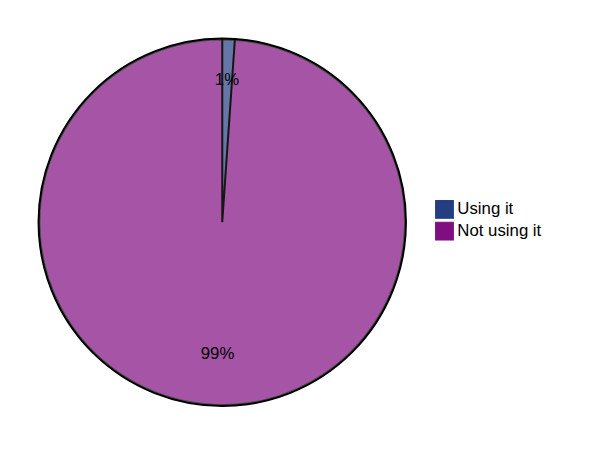
Global usage of header ‘cross-origin-embedder-policy’
Provide the distribution of usage of the header ‘cross-origin-embedder-policy’ across all domains analyzed.
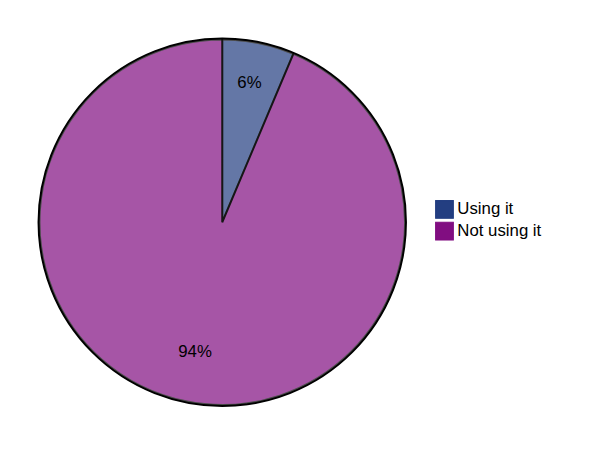
Global usage of header ‘cross-origin-embedder-policy-report-only’
Provide the distribution of usage of the header ‘cross-origin-embedder-policy-report-only’ across all domains analyzed.
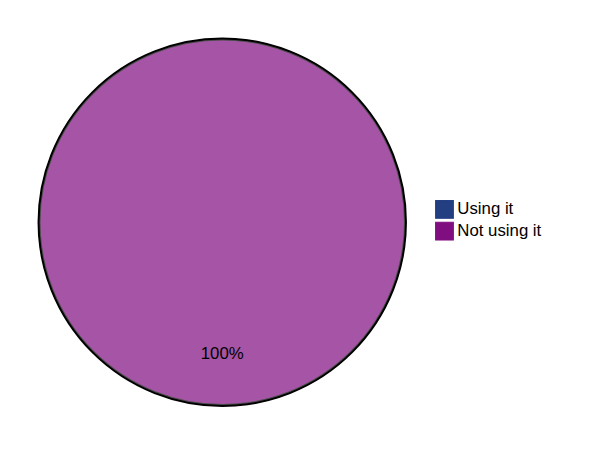
Global usage of header ‘cross-origin-opener-policy’
Provide the distribution of usage of the header ‘cross-origin-opener-policy’ across all domains analyzed.
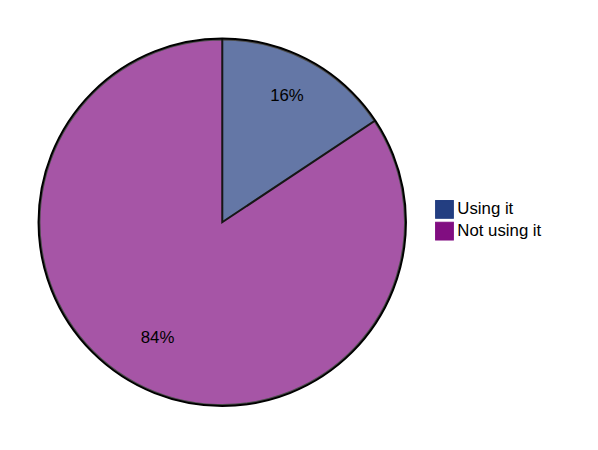
Global usage of header ‘cross-origin-opener-policy-report-only’
Provide the distribution of usage of the header ‘cross-origin-opener-policy-report-only’ across all domains analyzed.
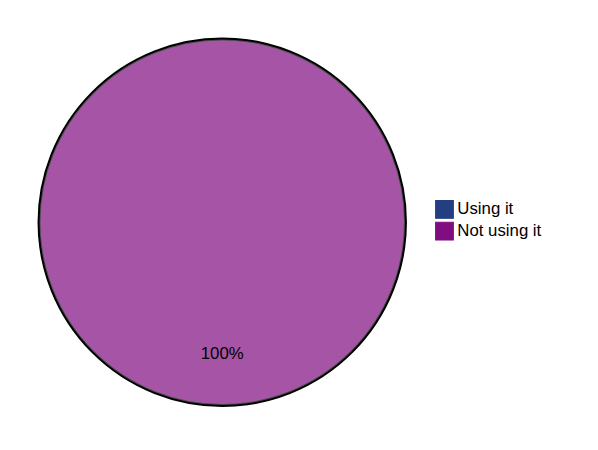
Global usage of header ‘cross-origin-resource-policy’
Provide the distribution of usage of the header ‘cross-origin-resource-policy’ across all domains analyzed.
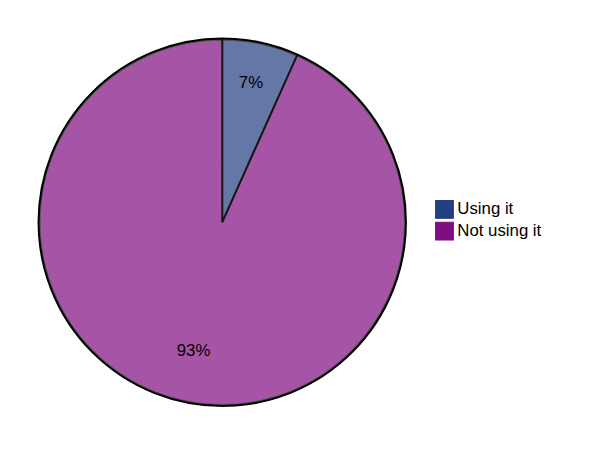
Global usage of header ‘expect-ct’
Provide the distribution of usage of the header ‘expect-ct’ across all domains analyzed.
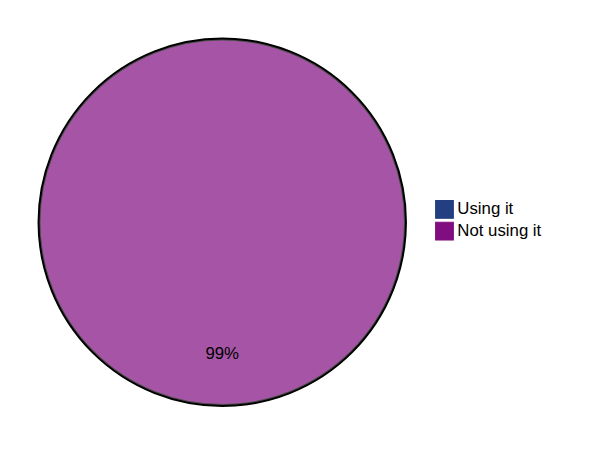
Global usage of header ‘integrity-policy-report-only’
Provide the distribution of usage of the header ‘integrity-policy-report-only’ across all domains analyzed.
Global usage of header ‘permissions-policy’
Provide the distribution of usage of the header ‘permissions-policy’ across all domains analyzed.
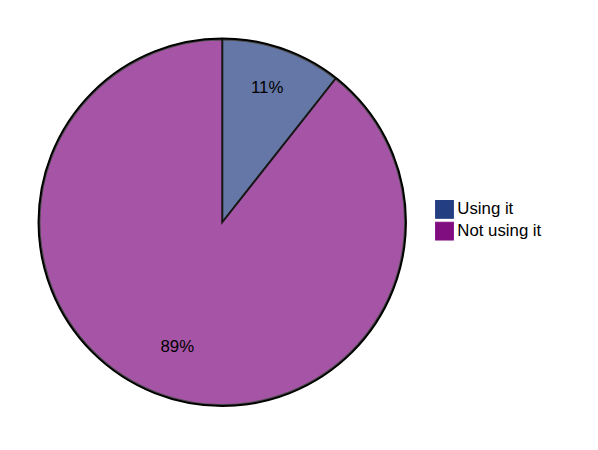
Global usage of header ‘permissions-policy-report-only’
Provide the distribution of usage of the header ‘permissions-policy-report-only’ across all domains analyzed.
Global usage of header ‘public-key-pins’
Provide the distribution of usage of the header ‘public-key-pins’ across all domains analyzed.
Global usage of header ‘referrer-policy’
Provide the distribution of usage of the header ‘referrer-policy’ across all domains analyzed.
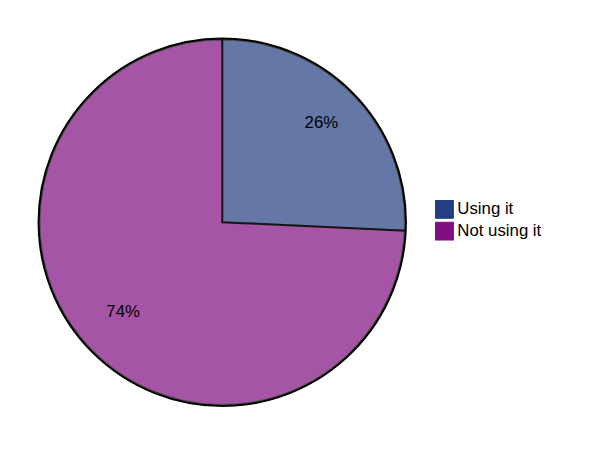
Global usage of header ‘strict-transport-security’
Provide the distribution of usage of the header ‘strict-transport-security’ across all domains analyzed.
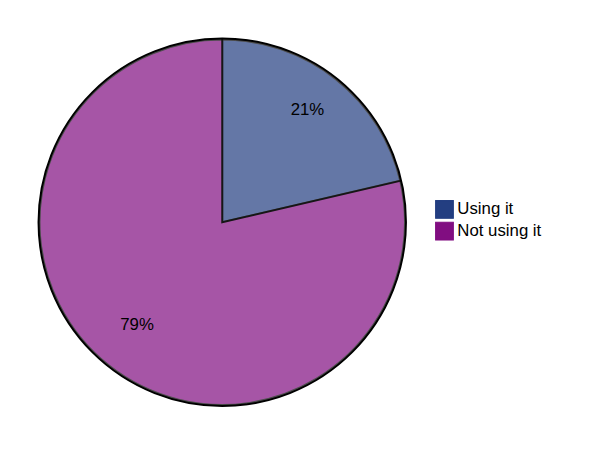
Global usage of header ‘x-content-type-options’
Provide the distribution of usage of the header ‘x-content-type-options’ across all domains analyzed.
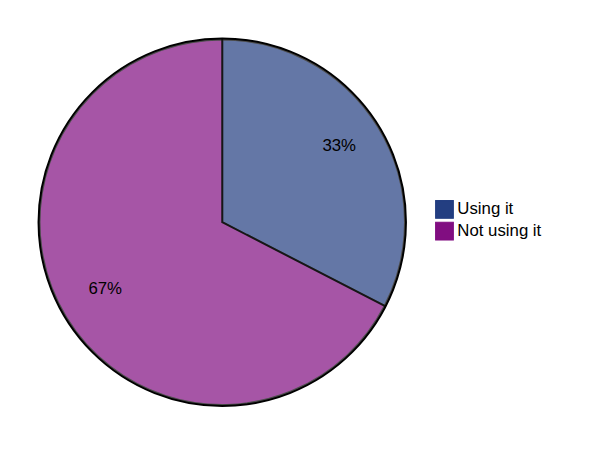
Global usage of header ‘x-dns-prefetch-control’
Provide the distribution of usage of the header ‘x-dns-prefetch-control’ across all domains analyzed.
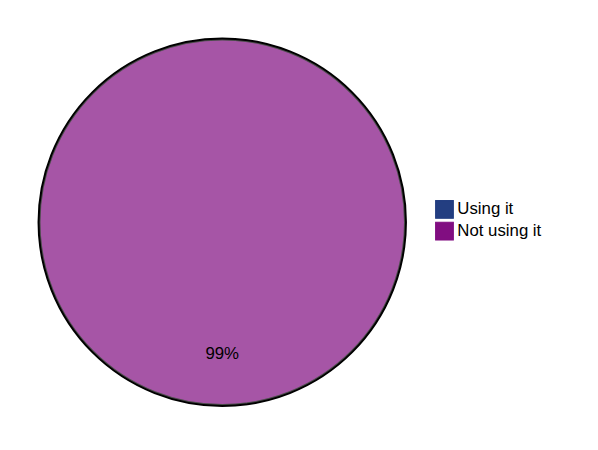
Global usage of header ‘x-frame-options’
Provide the distribution of usage of the header ‘x-frame-options’ across all domains analyzed.
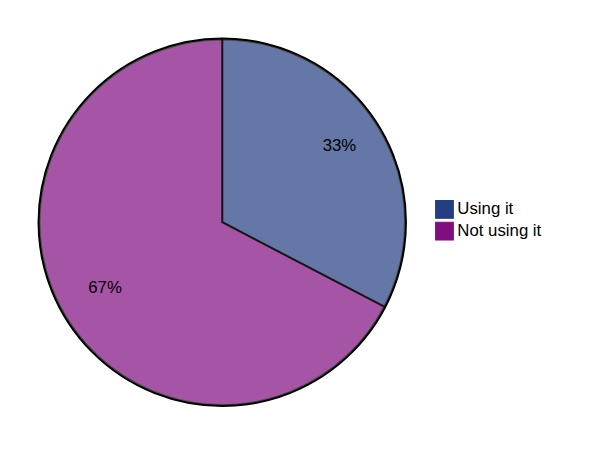
Global usage of header ‘x-permitted-cross-domain-policies’
Provide the distribution of usage of the header ‘x-permitted-cross-domain-policies’ across all domains analyzed.
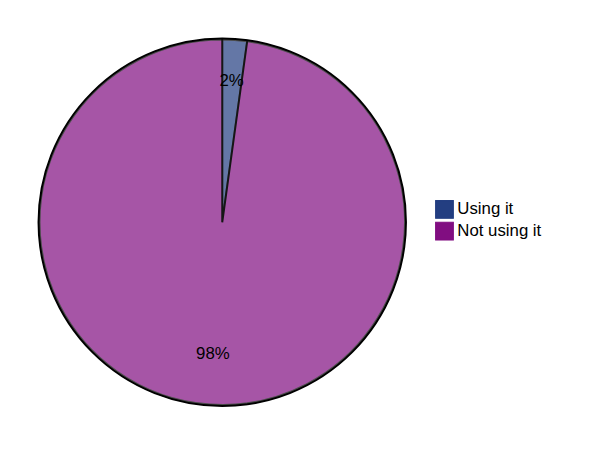
Global usage of header ‘x-xss-protection’
Provide the distribution of usage of the header ‘x-xss-protection’ across all domains analyzed.
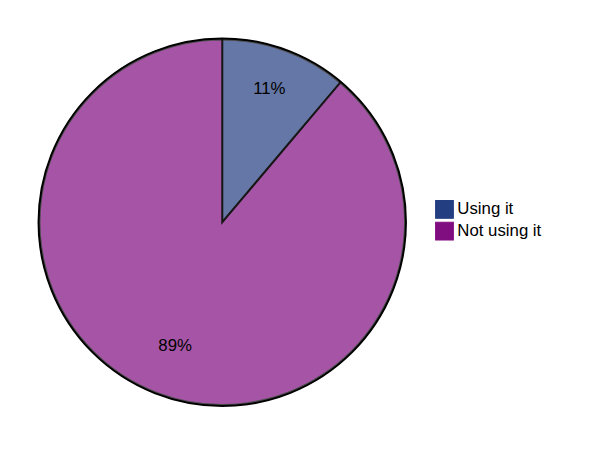
Global usage of insecure framing configuration via the header ‘x-frame-options’
Provide the distribution of usage of the header ‘x-frame-options’ across all domains analyzed with a insecure framing configuration: value different from DENY or SAMEORIGIN including unsupported values.
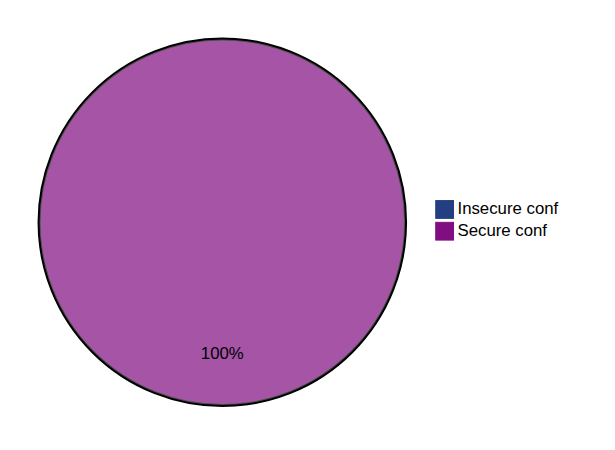
Global usage of insecure referrer configuration via the header ‘referrer-policy’
Provide the distribution of usage of the header ‘referrer-policy’ across all domains analyzed with a insecure referrer configuration: value set to unsafe-url or no-referrer-when-downgrade.
no-referrer-when-downgrade was included because it send origin, path, and querystring when the protocol security level stays the same (HTTPS is very often in place).
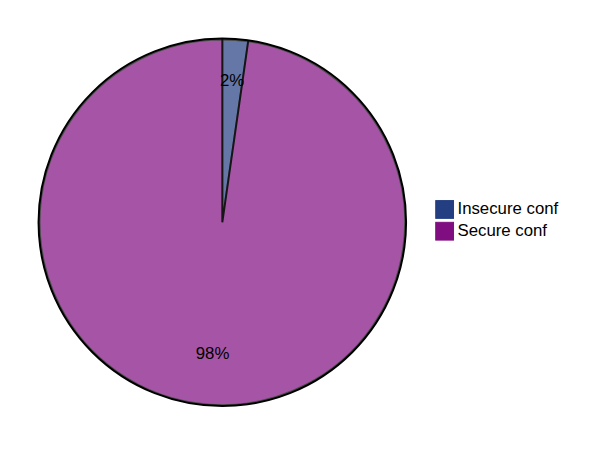
Global usage of the Strict Transport Security ‘preload’ feature
Provide the distribution of usage of the ‘preload’ feature for the header ‘strict-transport-security’ across all domains analyzed.
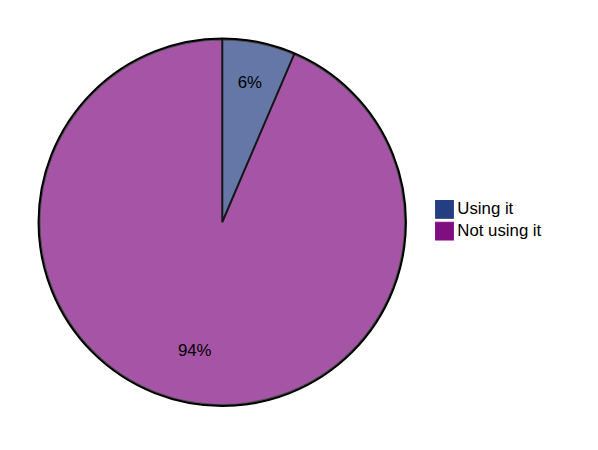
Global common ‘max-age’ values of the Strict Transport Security header
- Most common value used is 31536000 seconds (525600 minutes) across all domains analyzed.
- Maximum value used is 100000000000 seconds (1666666667 minutes) across all domains analyzed.
- Minimum value used is -471255354 seconds (-7854256 minutes) across all domains analyzed.
Global usage of content security policy with directives allowing unsafe expressions
Provide the distribution of content security policy allowing unsafe expressions across all domains analyzed.
Determine if a CSP policy contains (default-src|script-src|script-src-elem|script-src-attr|style-src) directives using (unsafe-inline|unsafe-hashes|unsafe-eval) expressions.
Based on Report-URI CSP generator allowed instructions for CSP directives.