About the current version
This is the current version of the OWASP DevSecOps Guideline. It explains how to build and operate a secure software delivery pipeline, promotes a shift-left (shift-everywhere) security culture, and curates vendor-neutral practices and tools for organizations of any size.
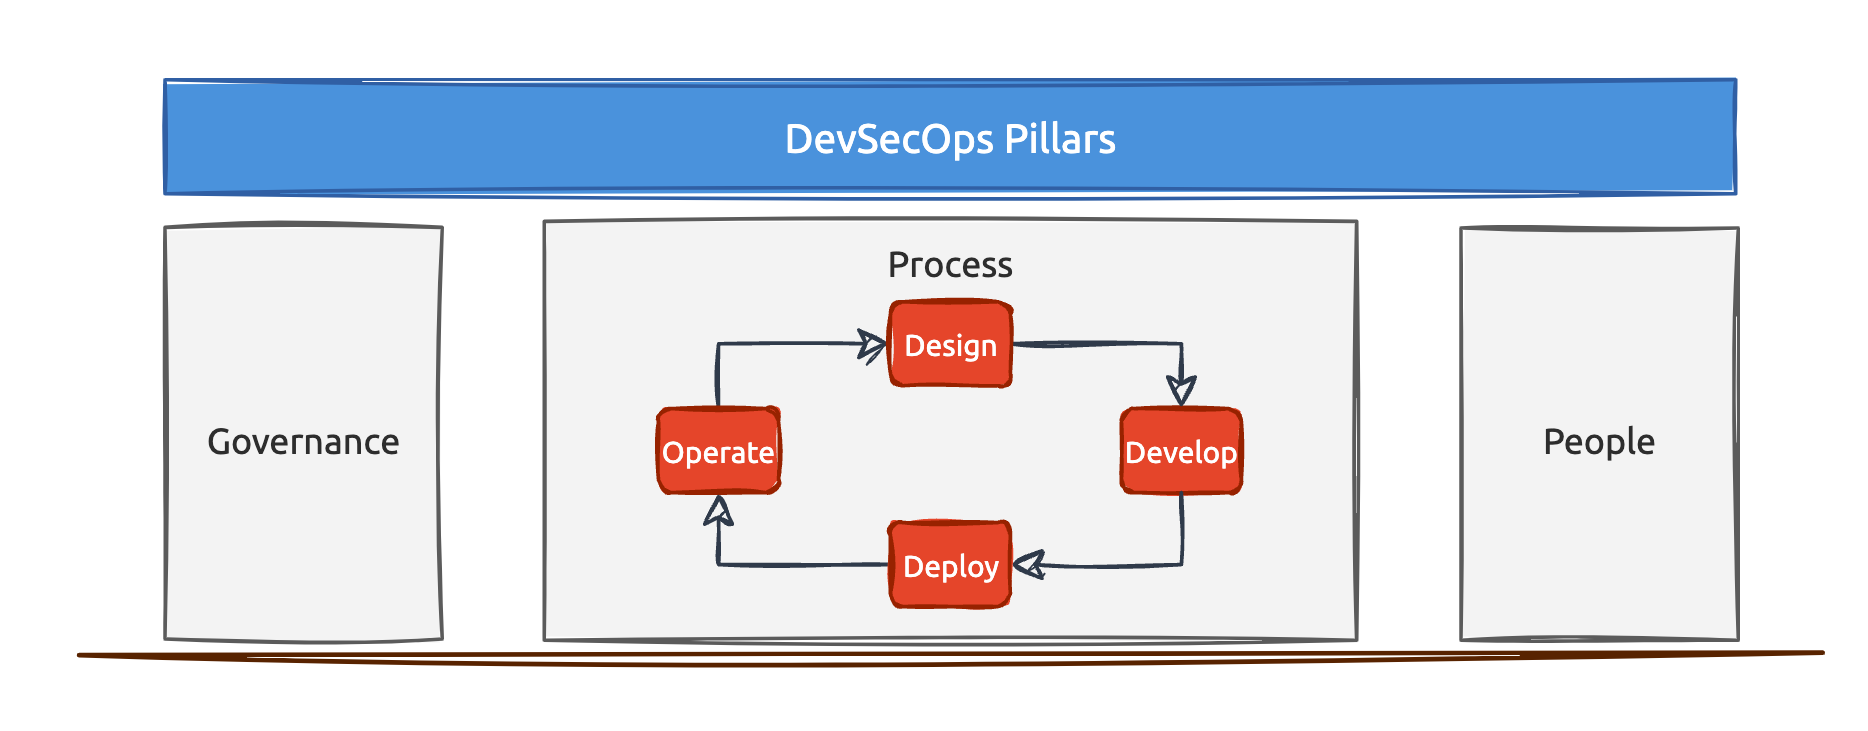
The guideline is organized around the three core pillars of DevSecOps:
- People — teams, roles, culture, and training.
- Process — security activities woven into every stage of the software development lifecycle.
- Governance — compliance, measurement, reporting, and oversight.
Under Process, the product development lifecycle is divided into seven stages: Design, Develop, Build, Test, Release, Deploy, Operate — with security controls mapped to each.
This revision refreshes every topic for 2025/2026 and adds coverage of modern concerns: software supply-chain security (SBOM, signing/provenance, CI/CD pipeline security), AI-assisted development and AI governance, Application Security Posture Management (ASPM), and explicit alignment with frameworks such as NIST SSDF, OWASP SAMM, OWASP DSOMM, and SLSA.
If you need earlier editions, see the old-versions directory.